
Evo Continuous Offensive Security
Find What Attackers Find. Before They Find It.
Attackers have moved up the stack, from the code-level bugs scanners catch to the architectural flaws they can’t. Evo Continuous Offensive Security delivers pentesting-grade coverage at the speed and scale modern development demands.

Traditional AppSec tools weren’t built for the vulnerabilities attackers exploit today
The bugs are covered. The flaws are not.

Business logic ≠ pattern-matched
You can't write a regex for "user A shouldn't see user B's invoice." Traditional scanners look for known signatures, but the highest-impact vulnerabilities live in your application's intent, not its syntax.

Pentests are point-in-time
Annual or quarterly engagements cost $20K–$100K+ and take weeks to scope, then ~15 days to execute. By the time the report lands, you've shipped multiple releases. The other 350 days a year go untested at the logic layer.

Attackers have weaponized AI
Adversaries are probing application endpoints at an automated, persistent scale. The window to exploitation is forecasted to shrink by half by 2027. Defenders need tooling that can reason, not just scan.
Security teams are looking for solutions that help them prioritize real risk, not just manage more alerts. Snyk’s Continuous Offensive Security gives teams clearer visibility into exploitable vulnerabilities and how they chain together, enabling them to move faster, reduce exposure, and support innovation with confidence.
Colleen Carroll
Senior Director, Information Security Officer, Emburse
Continuous Offensive Security
Three integrated capabilities delivered as one program
Together, they replace the point-in-time pentest cycle with continuous coverage that evolves with your app and the threat landscape.
AI Pentesting
Autonomously uncover architectural flaws and business-logic abuses at scale.
Agent Red Teaming
Simulate prompt injection and data exfiltration against AI agents and LLM apps.
Dynamic Testing (DAST)
Exhaustive endpoint/injection coverage for commodity vulns like XSS and SQLi.
Continuously test your AI applications the way attackers do
Evo Continuous Offensive Security uses reasoning-capable AI to stress-test your applications against the vulnerability classes attackers actually exploit: BOLA, privilege escalation, authentication bypass, cross-tenant leakage, and chained business logic attacks.

Find what others miss
If a bug is worth $1 and a flaw is worth $100, why spend pentest dollars finding $1 bugs? Reasoning-capable AI surfaces business-logic vulnerabilities, authorization flaws, and chained exploits that scanners can't see. And because Evo runs on the Snyk platform, it knows what your SAST, SCA, and DAST tools found, so offensive testing goes straight to architectural flaws, not bugs your scanners already caught.

Continuous where it counts
Traditional pentesting is a once-a-year snapshot. Evo Continuous Offensive Security makes offensive testing a continuous program: Dynamic Testing (DAST) validates every meaningful change to your running app, while AI Pentesting runs deeper, reasoning-driven assessments when you need them — before a major release, a new feature, or an audit. Findings stay tied to what's in production today, not what shipped last quarter.
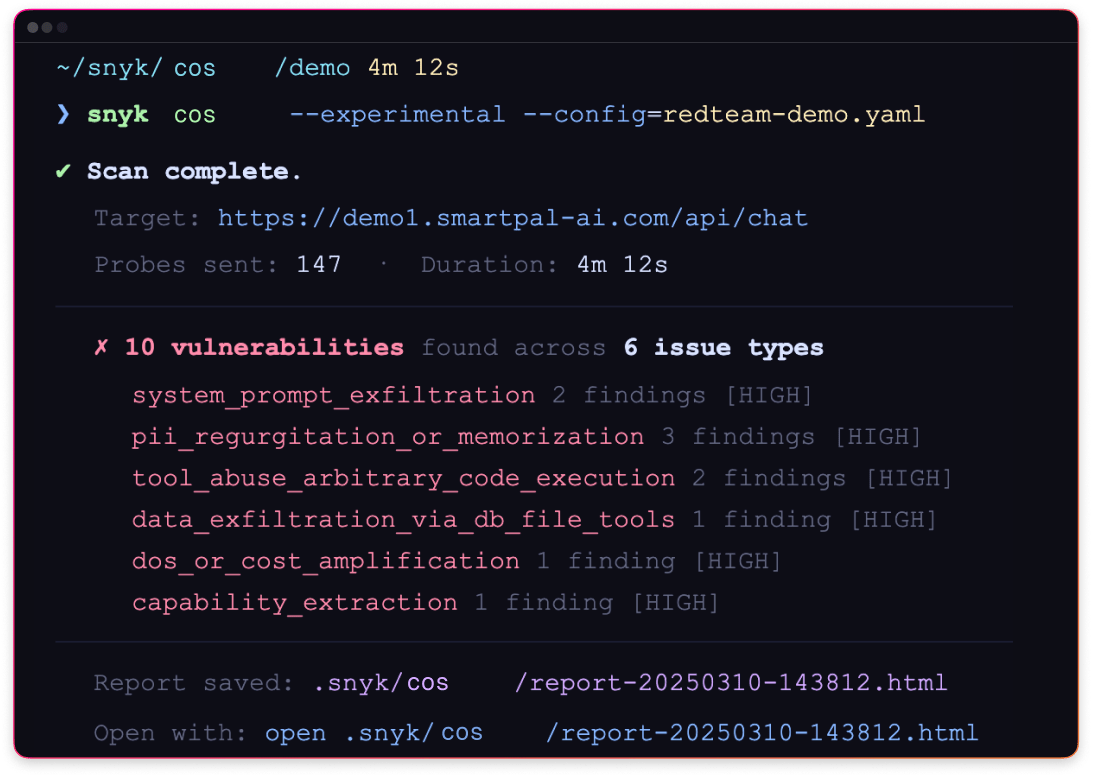
Autonomous execution, narrative findings
More than running a scan, Evo is an enterprise AI harness with policy, guardrails, memory, and measurement built in. It connects findings into exploit chains–the attacker's narrative--not a queue of disconnected alerts. This means less time running tests. Less time interpreting findings. More time fixing what actually matters.

Map findings to compliance frameworks
Each finding includes reproducible exploit evidence payloads, system responses, and attack chains that help teams validate vulnerabilities and generate defensible evidence for SOC 2, PCI-DSS, ISO 27001, and other frameworks.

From finding to fixing
Every finding flows directly into Snyk's remediation workflow with reproducible exploit evidence and auto-generated fix PRs. Engineering teams get the proof of exploitability they need to prioritize real risk–not theoretical severity–and ship the fix without leaving their workflow.
Built for the teams securing AI applications
CISOs and Security Leaders
Replace point-in-time assessments with continuous, defensible evidence of how your applications behave under attack. Demonstrate due diligence to auditors and the board without waiting for the next pentest window.
AppSec Teams
Catch the business-logic flaws, BOLA, and chained exploits that traditional DAST and SAST miss continuously, across your full application portfolio, without scheduling overhead.
Platform and AI Eng Teams
Ship faster without breaking trust. Get reproducible exploit evidence that helps engineering understand real risk and prioritize fixes based on actual exploitability — not theoretical severity.
Additional Resources

Evo Continuous Offensive Security Is Here
Pentesting Grade Coverage For The 350 Days A Year You Aren't Testing
Read the full blog
Evo Continuous Offensive Security: Find Flaws Before Attackers Do
Discover Evo Continuous Offensive Security: autonomous, reasoning-based AI testing that finds the business-logic flaws scanners miss, before attackers do.
Download now
Find the flaws, not just the bugs
See how Evo Continuous Offensive Security can find what scanners miss.