
Evo Agentic AppSec
Run the program, not the backlog
Evo Agentic AppSec puts a team of security agents next to every engineer, running the entire AppSec program end to end: understand, find, fix, and verify at the speed AI now builds and attacks software, with your team owning the bar.
Traditional AppSec was built for human speed and human volume
Finding issues and getting handed a backlog breaks down when code is generated continuously, and attacks are automated.
AI writes faster than review is possible
AI agents generate far more code than any team can read, and current models introduce several times more vulnerabilities per line than human developers. Manual review was already the bottleneck. Now it is not even in the running.
The backlog is now an attack surface
Years of unaddressed findings used to be a cleanup project. Attackers have gone agentic too: they enumerate backlogs and chain low-severity issues into critical exploits faster than any human team can respond.
Scanners are blind where AI code is weakest
The flaws AI introduces cluster in business logic, broken access control, and authentication. There is no known-bad pattern to match against, so pattern-based tools have nothing to find.
Relay Network cut remediation of a critical vulnerability from more than a week to under 24 hours, and holds a zero critical, zero high-severity posture across its codebase. “With the MCP server and Snyk, remediation has become much faster. We have tons of repositories, so being able to quickly go in, make fixes, and move on has significantly reduced remediation time.

Esaie Batoula
Security Engineer, Relay Network
A team of agents, each with one job, composed into one program
Agents execute, Snyk’s intelligence decides, and Snyk’s deterministic engines independently verify.
Code Scanning Agent
Combine AI reasoning with Snyk’s SAST to catch what pattern-matching structurally cannot, like complex logic flaws in AI-generated code.
Remediation Agent
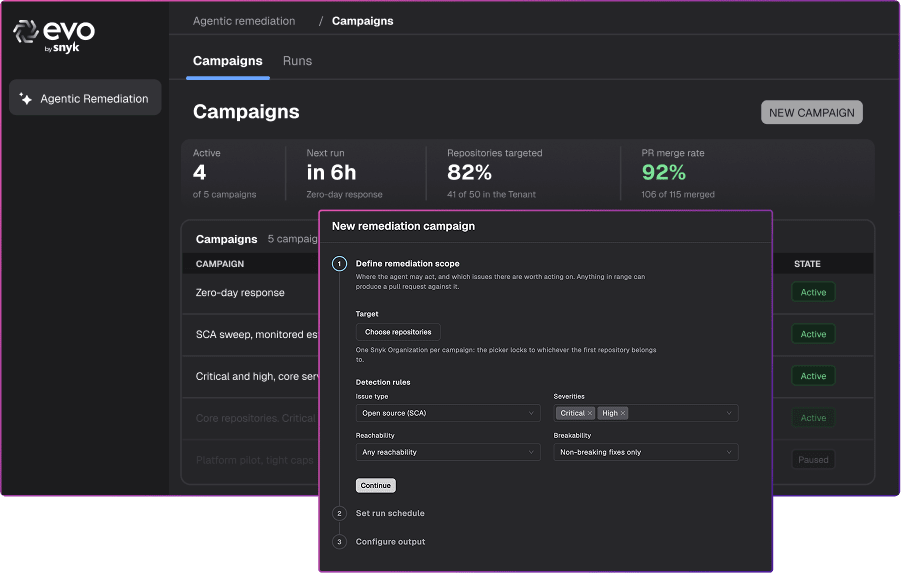
The callable find-to-fix agent: scan, fix, and validate, running in a sandbox with humans owning the merge bar across new code and the existing backlog.
Dependency Firewall
Install-time defense against malicious and out-of-policy packages, sitting between public registries and yours with caching, quarantine, and an audit trail.
Snyk Secrets
Leaked-secret prevention across the agentic development lifecycle, from IDE and pre-commit through PR checks and CI.
Agentic Security Review
An agent-driven security review of your repository: it builds an application and threat model, tests whether controls hold against credible threats, and delivers evidence-backed findings with clear remediation guidance.
How the program runs
Evo Agentic AppSec runs the full AppSec loop continuously, across both new code and everything already shipped. Each agent has one job and one trigger, grounded in a shared model of your application.
Understand and model the application
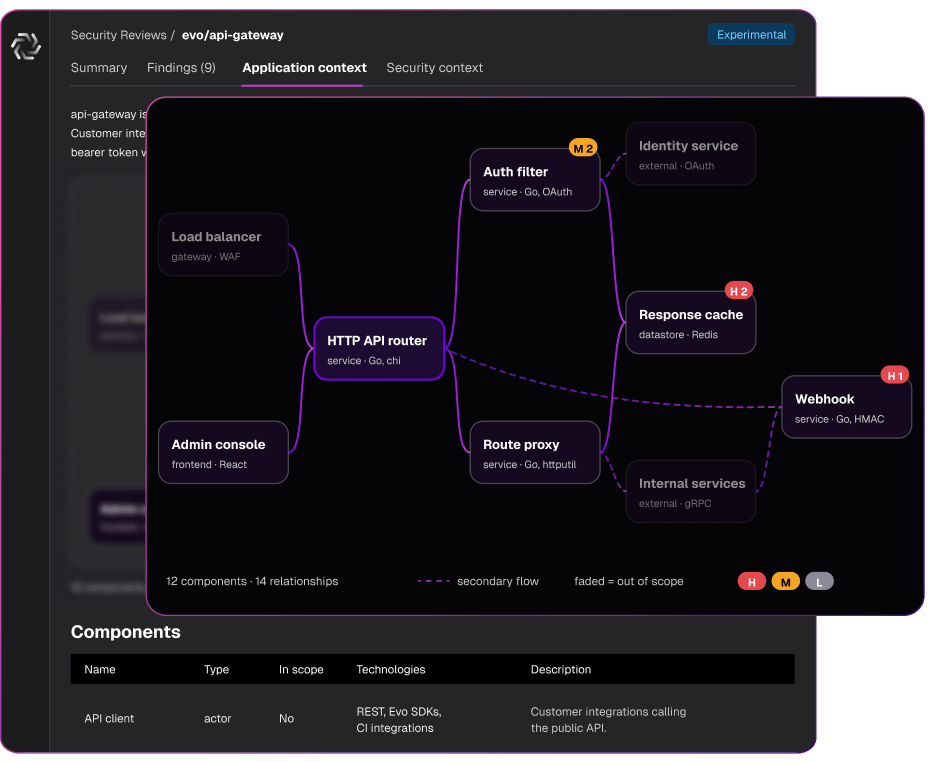
Agents build a living context graph of the application: architecture, data flows, classifications, trust boundaries, and what is actually running in production. From it, they derive a threat model that directs where to look first. Built once, updated as the code changes, read by every other agent.

Find what matters
Frontier reasoning runs next to Snyk’s deterministic engines to catch the business-logic and authorization flaws that scanners miss, plus leaked secrets. The context graph prevents agents from scanning everything blindly and burning tokens.

Prevent risk at the source
Stop new risk before it enters. Block malicious and out-of-policy packages at install time, and prevent secrets before they are committed. Extend this with Evo Agentic Development Security (ADS) to secure AI-generated code at inception inside the developer workflow.
Remediate and verify, with humans owning the bar
The remediation agent runs the full loop: scan, fix, and validate, with humans on the loop owning the merge bar. Snyk’s ten years of reachability, exploitability, breakability, and fix-outcome data is what turns a guessing model into an agent that ships fixes people actually merge. We see a 94% improvement in mergeable fix rate for SCA issues, 14% improvement for SAST, and 60% lower token cost when comparing Remediation Agent and a vanilla LLM.
Prove the fix holds
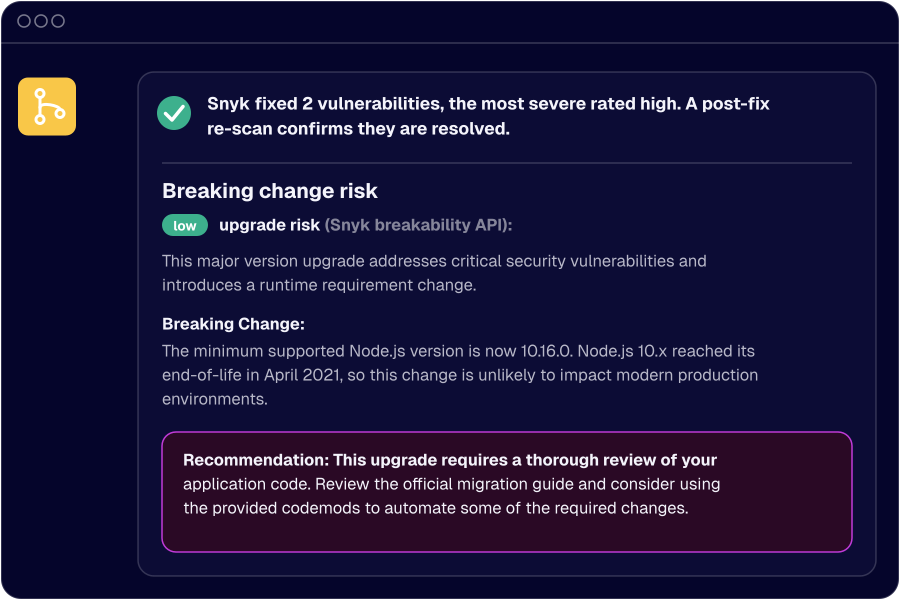
The agent that finds a vulnerability cannot be trusted to validate its own fix. Snyk’s deterministic engines are both the tools the agents call and the independent verifier of what they find, and every agent decision is captured in an audit trail.
The only vendor that runs the program, not just the scan
Competitors sell tools and hand you the integration and the backlog. Snyk pairs frontier AI reasoning with a substrate no one else has: a living context graph of your application and an intelligence layer built on ten years of reachability, exploitability, breakability, and fix-outcome data.
Snyk’s deterministic engines are both the callable tools the agents use and the independent verifier of what they find, which a competitor using one model to find and to grade its own fixes structurally cannot match. Snyk is also already inside the developer workflow, independent and vendor-neutral.
Built for the teams accountable for code that they no longer write by hand
AppSec and ProdSec leads
Run the program, not the backlog. A team of agents runs the whole AppSec loop. Get validated, mergeable fixes at scale, with the backlog trending down. Frontier detection is built for what scanners cannot see. Get an audit trail for every agent decision.
Developers
Ship fast, and let agents secure AI-generated code at inception, inside your IDE, and your agent. Get validated, mergeable fixes you approve, not write. Evo AAS meets you where you work: repo, CLI, or code agent.
CISOs and security leaders
Defense at the speed of offense. Get a continuous, adversarially tested, auditable program, and reduce systemic risk without scaling headcount. Independent and vendor-neutral across every coding agent.
Run the program, not the backlog.
See how a team of security agents burns down your backlog and secures what AI writes next.
Additional Resources


Run the Program, Not the Backlog: Retiring the Compromise at the Heart of AppSec
Download now
Find the flaws, not just the bugs
See how Evo Continuous Offensive Security can find what scanners miss.